
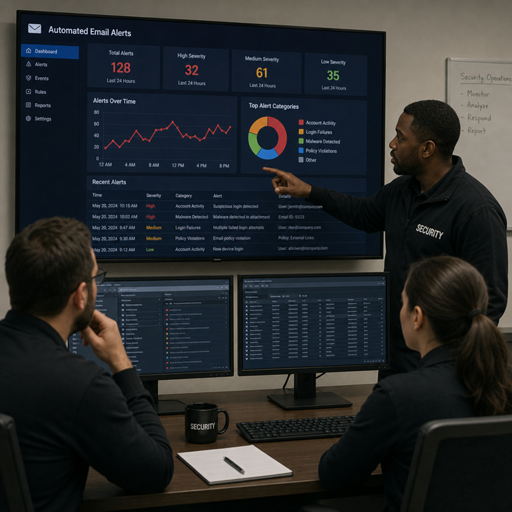
Email threats move quickly, and your team needs to know when something suspicious happens—not hours later, not after a user reports it. Automated email security alerts help surface risky activity, policy violations, and unusual patterns so the right people can respond with confidence. This page explains how a practical alerting setup works and what to put in place before you rely on automated email protection for day-to-day defense.
What should automated email security alerts tell your team?
Automated email security alerts should tell your team what happened, why it matters, who or what is affected, and what action should happen next. A useful alert does more than say “threat detected.” It gives enough context for a security, IT, or operations lead to decide whether to investigate, block, quarantine, notify a user, or escalate.
The goal is not to create more noise. The goal is to create a dependable signal when email activity points to phishing, malware, credential theft, spoofing, data exposure, or account misuse. Strong security alert automation helps your team act earlier while reducing the manual work of checking dashboards, logs, and inboxes throughout the day.
A smarter way to monitor email risk
Email remains one of the most common places where users encounter suspicious links, attachments, impersonation attempts, and social engineering. Manual monitoring is rarely enough because threats can arrive at any time, and busy teams cannot inspect every message in real time. Automated alerts create a structured response layer between detection and action.
With the right configuration, alerts can be triggered when a message matches known risk conditions, when user behavior changes, or when a policy boundary is crossed. For example, an alert might notify an administrator when multiple users receive a similar suspicious message, when an executive impersonation attempt is detected, or when a user clicks a link that has been reclassified as unsafe.
This is where automated email protection becomes operationally useful. It does not simply block or filter messages in the background. It gives your team visibility into events that deserve attention, making email security easier to manage and easier to improve over time.
Core alerts worth setting up first
Start with the alerts that connect directly to common risks and response decisions. A smaller set of well-tuned automated alerts is usually more useful than a long list that no one reviews consistently.
Consider setting up alerts for:
- Phishing indicators: Messages that contain suspicious links, spoofed sender details, urgent payment language, or credential-harvesting patterns.
- Malware and attachment risk: Attachments flagged by scanning tools, file types that violate policy, or messages containing links to downloadable payloads.
- Impersonation attempts: Emails that appear to imitate executives, finance staff, vendors, support teams, or internal systems.
- Account compromise signals: Unusual sending patterns, unexpected forwarding rules, repeated login failures, or sudden outbound email spikes.
- Sensitive data exposure: Messages that appear to include confidential files, personal data, financial information, or other protected content.
- Quarantine and release events: Admin or user actions that release blocked messages, especially when the message was originally considered high risk.
These alerts give your team a practical starting point. They cover the most important situations where speed, context, and accountability matter.
How the setup process works
A good implementation begins with understanding your email environment, your risk tolerance, and who should be notified when different events occur. Not every alert belongs with the same person. A suspected phishing campaign may need security review, while a data handling alert may need an IT, compliance, or department lead to take action.
A practical setup usually follows this flow:
- Map your email risks. Identify the threats, policy concerns, and user behaviors that matter most to your organization.
- Define alert categories. Separate critical, high, medium, and informational alerts so urgent events do not get buried.
- Choose recipients and channels. Decide whether alerts should go to email, a ticketing system, chat, a security platform, or a shared operations queue.
- Set clear trigger conditions. Use rules that are specific enough to be useful but flexible enough to catch meaningful variations.
- Add response guidance. Include recommended next steps so recipients know whether to investigate, contain, document, or escalate.
- Test before relying on it. Send controlled examples, review routing, and confirm that the alert contains the right context.
- Review and tune regularly. Reduce false positives, add missing scenarios, and adjust severity as your environment changes.
This approach keeps security alert automation connected to actual workflows. Instead of creating alerts simply because a tool can generate them, you build alerts around decisions your team needs to make.
Alert quality determines response quality
A vague alert slows people down. A clear alert shortens the path from detection to action. The best automated email security alerts include enough information to make the next step obvious without requiring the recipient to search across several systems first.
A strong alert should include:
- The affected user, mailbox, group, or domain
- The sender, subject line, message ID, or other identifying details
- The reason the event was flagged
- Severity level and confidence level, if available
- Message status, such as delivered, blocked, quarantined, or removed
- Recommended action and escalation path
- Links to investigate, review logs, or open a response ticket
This structure helps both technical and non-technical stakeholders. An administrator can investigate quickly, while a manager can understand the business impact without needing to decode raw security data.
Built for teams that need fast, consistent action
Automated alerts are especially valuable when responsibility is shared across IT, security, help desk, compliance, and business teams. Without automation, one person may spot a suspicious pattern while another misses the related event. With automated email protection and consistent alert routing, the response process becomes more predictable.
For a small team, this may mean getting a clear notification when a high-risk message reaches an inbox. For a growing organization, it may mean routing different alert types to different queues and documenting every response. For a distributed workforce, it may mean identifying suspicious email activity even when users are working in different locations and time zones.
The practical benefit is focus. Your team spends less time wondering what happened and more time deciding what to do about it.
Common mistakes to avoid
Many alerting programs fail because they start too broad. If every minor event creates an urgent notification, people stop paying attention. If alerts lack ownership, everyone assumes someone else is handling the issue.
Avoid these common problems:
- Sending every alert to the same inbox without severity levels
- Creating rules that trigger too often for low-risk activity
- Failing to document who owns each alert type
- Leaving out recommended next steps
- Not testing alerts after policy or platform changes
- Ignoring false positives until users lose trust in the system
Good security alert automation is not “set it and forget it.” It should improve as your organization learns which alerts lead to meaningful action and which ones only create noise.
Start with a clear alerting plan
You do not need a complicated program to begin. Start by identifying the email events your team most needs to know about, decide who should receive each alert, and build a simple response path for every high-priority scenario. Once the foundation is working, you can expand into more advanced automated alerts and richer integrations.
If you are ready to strengthen automated email protection, begin with an alerting plan that fits your team’s real workflow. Define the threats you want to catch, the actions you want to trigger, and the people who need to be involved. Then turn those decisions into automated email security alerts your organization can trust.
