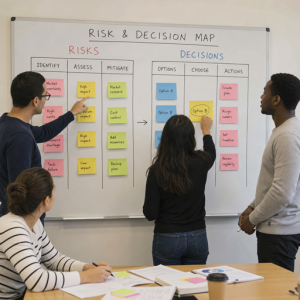
A post-mythos action plan helps teams move from story-driven momentum to practical readiness before the next wave of changes arrives. Whether the “patch wave” means
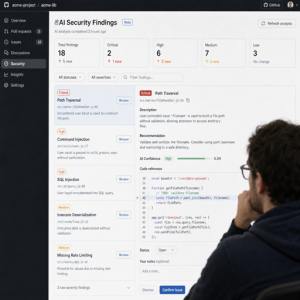
Anthropic has introduced OSS Scanner, a free, opt-in AI vulnerability scanner for open-source projects that want faster vulnerability assessment using Anthropic’s strongest models. The service
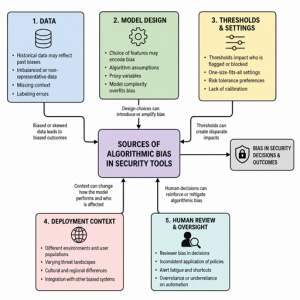
Security tools increasingly use machine learning, rules engines, scoring models, biometrics, behavioral analytics, and generative AI to decide what looks risky. Algorithmic bias in security
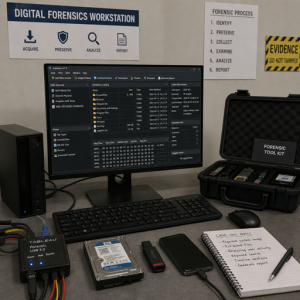
Open-source forensics kits bring together the forensic tools, workflows, and utilities investigators use to collect, preserve, examine, and explain digital evidence. They can support cyber
Small businesses need security tools that protect real work without slowing every task to a crawl. The right setup keeps file sharing, mobile access, passwords,
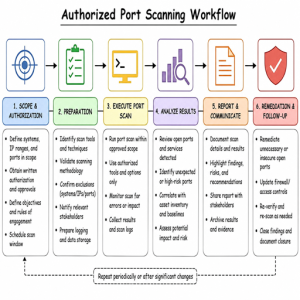
Open-source port scanning utilities help security teams, administrators, and curious learners understand which services are reachable on a network. Used responsibly, they turn unknown exposure
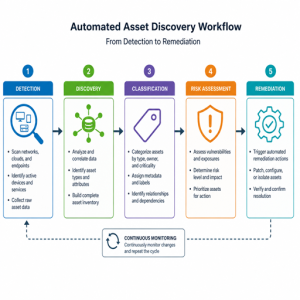
You cannot secure what you cannot see. Automated asset discovery gives security and IT teams a living inventory of devices, cloud resources, applications, users, services,
Threat hunting works best when analysts can ask better questions of their data, test hypotheses quickly, and preserve evidence as an investigation develops. Open source
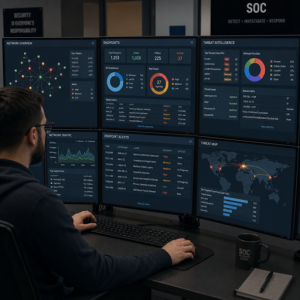
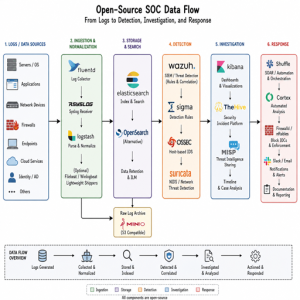
An open-source SOC is a security operations center built with community-driven, transparent, and customizable technologies instead of relying entirely on proprietary platforms. The goal is
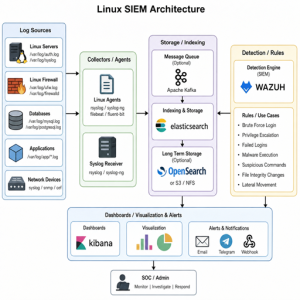
n open-source SIEM on Linux gives teams a practical way to collect logs, detect suspicious activity, investigate incidents, and improve visibility without starting with a