
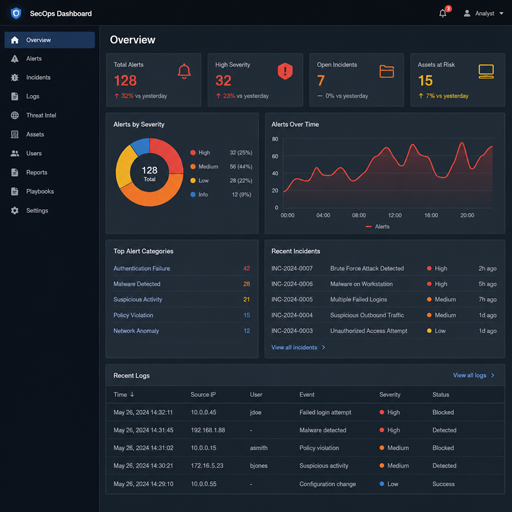
Open source security management tools help teams monitor systems, investigate suspicious activity, centralize logs, and improve security operations without starting from a fully proprietary stack. The best fit depends on whether you need endpoint visibility, network monitoring, log correlation, compliance support, or a complete open source SIEM environment. This list walks through practical options and how to evaluate them for real-world information security management.
Which open source security management tools should you evaluate first?
Start with the tool that matches your most urgent security gap. If you lack centralized alerting, prioritize an open source SIEM or log management platform. If you cannot see endpoint activity, begin with an agent-based platform. If your biggest blind spot is network traffic, choose a network security monitoring stack before adding more dashboards.
A smart shortlist usually includes tools from three categories:
- SIEM and log correlation: for centralizing events, searching incidents, and building alerts.
- Endpoint and host monitoring: for file integrity, configuration checks, vulnerability signals, and suspicious behavior.
- Network and threat detection: for packet visibility, intrusion detection, and traffic analysis.
The tools below are not identical substitutes. Some are full security platforms, while others are focused building blocks that become powerful when combined.
1. Wazuh supports endpoint monitoring and open source SIEM workflows
Wazuh is often one of the first tools teams review when researching open source security information management because it combines agent-based endpoint visibility with log analysis and alerting. It can help security teams monitor hosts, review events, detect policy issues, and investigate activity across servers, cloud workloads, and user endpoints.
Its practical strength is coverage. Teams can use it for file integrity monitoring, configuration assessment, vulnerability-related visibility, and security event collection. For organizations trying to mature from scattered logs into structured security information management, that breadth can reduce the number of separate tools needed at the beginning.
Wazuh is a strong candidate when you want:
- Endpoint agents across Linux, Windows, or cloud systems.
- Centralized security alerts from hosts and applications.
- Compliance-oriented monitoring without building everything from scratch.
- A platform that can integrate with search and visualization components.
It still requires planning. Alert tuning, storage sizing, agent deployment, and rule management can become complex as environments grow. Treat Wazuh as a platform to operate, not a simple plug-in.
2. Security Onion gives teams a full network security monitoring stack
Security Onion is useful for teams that need broad visibility into network traffic, intrusion detection alerts, and security logs. Instead of being a single-purpose utility, it brings together multiple open source security components into a packaged platform designed for detection and investigation.
This makes it attractive for security operations centers, labs, managed environments, and teams that want to learn how different detection layers work together. Network metadata, alerts, packet evidence, and logs can help analysts move from “something happened” to “what happened, where, and how.”
Security Onion is especially valuable when your team needs to:
- Monitor north-south or internal network traffic.
- Investigate suspicious connections and intrusion alerts.
- Practice analyst workflows in a realistic environment.
- Combine network evidence with logs and endpoint signals.
The tradeoff is operational weight. Network sensors, storage, retention, packet capture, and alert volume must be designed carefully. For small teams, it may be better to start with a limited deployment than to collect everything immediately.
3. AlienVault OSSIM offers an accessible open source SIEM foundation
AlienVault OSSIM is a familiar name for teams exploring open source SIEM solutions. It was built to bring several security monitoring functions into one environment, including event collection, correlation, asset discovery, vulnerability assessment concepts, and intrusion detection integrations.
Its main appeal is that it introduces SIEM-style thinking in a consolidated package. Teams that are new to security information management can use it to understand how assets, events, rules, and investigations connect. It can be helpful in labs, smaller environments, and educational settings where learning the SIEM model matters as much as production scale.
Consider it when you want:
- A recognizable open source SIEM entry point.
- A combined view of assets, alerts, and security events.
- A way to learn core SIEM workflows before expanding.
- A platform that demonstrates correlation and monitoring concepts.
As with any older or long-running open source software project, evaluate the current community, documentation, integrations, and maintenance model before committing. Security tools age quickly if rules, parsers, and deployment practices are not actively reviewed.
4. Elastic Stack can become a flexible security analytics platform
Elastic Stack is not only a security tool; it is a search, analytics, and visualization stack that many teams adapt for security logging. Its value comes from ingesting large volumes of data, searching across it quickly, and building dashboards that help analysts spot patterns.
For open source security use cases, Elastic-style architecture can support log centralization, detection engineering, dashboards, and investigation workflows. Teams often connect system logs, application logs, cloud events, authentication records, and network telemetry, then write rules or searches to identify suspicious behavior.
It fits best when your team has the skills to design and maintain data pipelines. You need to think about parsing, index strategy, retention, access control, alert quality, and storage costs. Without that discipline, flexible log management can become a noisy data lake.
Use it when you need:
- Custom dashboards for security and operations teams.
- Fast search across many event sources.
- Flexible ingestion pipelines.
- A foundation that can support security analytics beyond basic alerts.
Elastic-based approaches are powerful, but they reward teams that invest in data quality. Clean fields, consistent naming, and reliable parsing are what turn logs into useful security information.
5. Graylog helps centralize logs for practical investigations
Graylog is a log management platform that can support many information security management tasks. It is often used to collect, parse, search, and alert on logs from systems, applications, firewalls, authentication services, and other infrastructure.
For security teams, Graylog can be a pragmatic step toward better visibility. You may not need a complete SIEM on day one. Sometimes the immediate problem is simply that logs are scattered across servers, devices, and cloud services, making incident response slow and incomplete.
Graylog can help teams:
- Centralize logs from diverse sources.
- Build searches for common incident questions.
- Create alerts for high-risk events.
- Give IT and security teams a shared view of activity.
Its best use is often focused. Start with high-value log sources such as authentication, privileged access, endpoint security, firewalls, VPNs, and critical applications. A smaller set of well-parsed logs is more useful than a huge volume of unstructured noise.
6. Zeek adds deep network visibility for detection and response
Zeek is a network analysis framework used to understand what is happening across network traffic. Rather than acting only as a signature-based intrusion detection tool, it produces rich protocol logs and metadata that analysts can use during investigations.
This makes Zeek valuable in open source security architectures that need context. For example, authentication attempts, DNS behavior, HTTP activity, connection records, and file-related observations can support threat hunting and incident response. When paired with a SIEM or log platform, Zeek data can help explain the network side of an alert.
Zeek is a strong choice when you want:
- Detailed network metadata rather than only alerts.
- Evidence for threat hunting and timeline reconstruction.
- Visibility into protocols and unusual communication patterns.
- Data that can enrich open source security information management workflows.
The main challenge is volume and interpretation. Zeek can generate a lot of data, and teams need clear use cases to avoid drowning in telemetry. Begin with defined detection questions, then expand coverage as your analysts learn which logs matter most.
7. Suricata provides intrusion detection and prevention capabilities
Suricata is a widely used open source intrusion detection and intrusion prevention engine. It inspects network traffic and can generate alerts based on rules, signatures, and protocol analysis. For many teams, it is a core component of an open source security monitoring stack.
Suricata is useful because it gives security teams a direct way to detect known malicious patterns, suspicious traffic, policy violations, and exploit attempts. When its alerts are sent into an open source SIEM or log platform, analysts can correlate them with endpoint activity, user behavior, and firewall logs.
It is most effective when paired with strong rule management. Too many untuned alerts will overwhelm analysts; too few rules may miss important behavior. Teams should review rule sources, suppress known false positives, and prioritize alerts that map to their actual environment.
Suricata works well for:
- Network intrusion detection.
- Alert enrichment in SIEM solutions.
- Monitoring traffic at key network points.
- Building layered detection with Zeek, Wazuh, or Security Onion.
It is not a complete security program by itself. Think of it as a high-value detection engine inside a broader information security management strategy.
8. TheHive improves incident response and case management
TheHive is designed for security incident response and case management. While SIEM tools help collect and alert on events, incident response platforms help teams organize what happens next: triage, investigation, task ownership, evidence tracking, and closure.
This distinction matters. Many organizations have alerts but lack a consistent process for handling them. TheHive can help analysts move from reactive inbox management to structured casework, especially when paired with alert sources, enrichment tools, and threat intelligence feeds.
Use TheHive when your team needs to:
- Turn alerts into trackable cases.
- Assign investigation tasks and document decisions.
- Preserve evidence and analyst notes.
- Standardize response workflows across incidents.
It is especially helpful once alert volume grows. Even a strong open source SIEM can lose value if investigations are handled in chat threads and spreadsheets. Case management gives the human side of security operations a clearer operating model.
9. MISP supports threat intelligence sharing and enrichment
MISP, the Malware Information Sharing Platform, helps teams collect, structure, share, and use threat intelligence. In practical terms, it can store indicators, threat context, relationships, and event information that support detection and investigation.
For open source security programs, MISP is valuable because alerts are more useful when analysts understand what they relate to. An IP address, domain, hash, or email artifact may be more meaningful when connected to a campaign, malware family, or known threat behavior. That context can improve triage and prioritization.
MISP can support:
- Internal threat intelligence repositories.
- Indicator sharing between trusted groups.
- Enrichment for SIEM alerts and investigations.
- Better context for incident response teams.
The important caution is quality control. Threat intelligence is not automatically useful because it is abundant. Teams should define what they collect, how they validate it, when indicators expire, and how intelligence feeds into security operations.
10. osquery turns endpoints into queryable security data sources
osquery lets teams query endpoints using SQL-like syntax, making it useful for security investigations, compliance checks, and operational visibility. Instead of waiting for a single-purpose alert, analysts can ask targeted questions about processes, users, startup items, network connections, packages, and system configuration.
This is powerful for teams that want flexible endpoint visibility without relying only on predefined detections. During an investigation, osquery can help confirm whether a suspicious process exists, whether a configuration changed, or whether a certain artifact appears across multiple machines.
It works best when integrated into a broader management approach. Teams need a way to deploy it, schedule queries, collect results, and control access. Query design also matters because poorly planned queries can create noise or performance concerns.
osquery is useful for:
- Endpoint investigation and hunting.
- Configuration and asset visibility.
- Checking for known indicators across systems.
- Supporting incident response with targeted questions.
As part of an open source security toolkit, it gives analysts a flexible way to interrogate endpoints when standard logs are not enough.
A practical comparison for choosing the right tool
Choosing between tools is easier when you map each option to the job it performs. The table below simplifies the decision without pretending every platform does only one thing.
|
Need |
Tools to consider |
Best starting point |
|---|---|---|
|
Centralized endpoint security monitoring |
Wazuh, osquery |
Deploy agents to critical systems first |
|
Full open source SIEM exploration |
Wazuh, AlienVault OSSIM, Elastic Stack |
Start with a lab or limited production scope |
|
Network intrusion detection |
Suricata, Security Onion |
Monitor one important network segment |
|
Network metadata and hunting |
Zeek, Security Onion |
Define investigation questions before collecting everything |
|
Log management and search |
Graylog, Elastic Stack |
Prioritize authentication and privileged access logs |
|
Incident response coordination |
TheHive |
Standardize triage and case documentation |
|
Threat intelligence management |
MISP |
Curate high-quality indicators and context |
The right stack is usually layered. A team might use Suricata for detection, Zeek for network context, Wazuh for endpoint visibility, Graylog or Elastic for searchable logs, and TheHive for case management. Another team may need only one or two tools to close its biggest gaps.
Open source security tools work best with a clear operating model
Open source software can reduce licensing barriers, increase transparency, and give teams more control over their security architecture. However, open source does not remove the need for ownership. Someone still has to maintain systems, update rules, tune alerts, review logs, manage storage, and document response processes.
Before deploying any open source security information management platform, define the basics:
- Primary use case: detection, compliance, investigation, threat hunting, or learning.
- Data sources: endpoints, firewalls, identity systems, cloud logs, applications, or network sensors.
- Retention needs: how long logs must remain searchable and why.
- Alert ownership: who receives alerts, triages them, and escalates incidents.
- Success criteria: fewer blind spots, faster investigations, better audit evidence, or clearer response workflows.
- Maintenance plan: updates, backups, rule tuning, access control, and documentation.
This planning prevents tool sprawl. Many teams install multiple SIEM solutions or monitoring platforms, then struggle because no one defined what each tool should do. A smaller, well-managed stack will usually outperform a larger collection of neglected dashboards.
Where should your team start?
Start with the visibility gap that creates the most risk today. If you cannot answer who logged in, what changed, or which systems generated critical alerts, begin with log collection and endpoint monitoring. If you cannot investigate suspicious network behavior, add network detection and metadata sources before expanding into advanced automation.
A simple rollout plan can keep the project manageable:
- Pick one priority environment. Start with critical servers, identity systems, or a key network segment.
- Collect only useful data first. Focus on logs and events that support real investigations.
- Tune alerts before expanding. Reduce false positives so analysts trust the system.
- Document response steps. Decide how alerts become cases, tasks, and lessons learned.
- Review the stack regularly. Retire unused integrations and improve the ones that help.
Open source security management is not about finding one perfect tool. It is about building a practical, maintainable system that helps your team see risk sooner, investigate with confidence, and improve security operations over time.
