
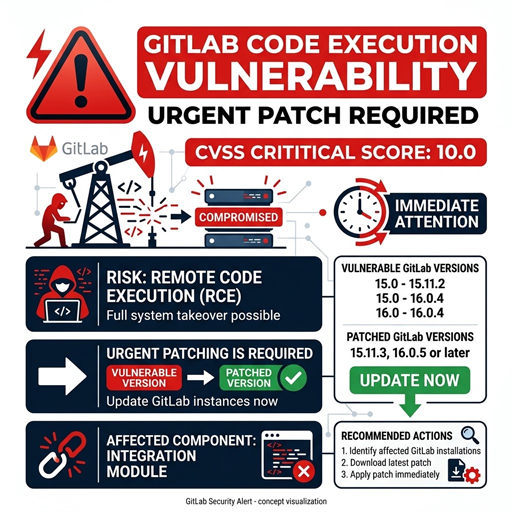
GitLab has issued an urgent GitLab security patch for a maximum-severity flaw that could allow unauthenticated code execution on vulnerable self-managed GitLab servers. The GitLab vulnerability, tracked as CVE-2026-97229, affects GitLab Community Edition and Enterprise Edition in several 19.x release lines and is fixed in newly released patch versions. Administrators running affected self-managed instances should treat the GitLab patch update as a priority because the flaw sits in the CI/CD path, where a server compromise can quickly become a software supply chain problem.
What happened?
GitLab released patched versions of GitLab CE/EE on October 12, 2026, to address a critical integer overflow issue in the CI/CD Regular Expression Compiler. The GitLab code execution vulnerability could, under certain conditions, let an unauthenticated attacker execute arbitrary code on the GitLab server by using a specially crafted regular expression in a CI/CD configuration. GitLab assigned the issue a CVSS 3.1 score of 10.0, the highest severity rating, and credited the researcher using the handle “joaxcar” for reporting it through GitLab’s HackerOne bug bounty program.
The current GitLab advisory lists fixed versions as 19.4.2, 19.3.5, and 19.2.8. Earlier summaries and third-party advisories referenced 19.3.4 for the 19.3 line, but GitLab’s current release notes say 19.3.4 had a bug affecting merge request pages when the Ona integration was enabled, and that the issue is fixed in 19.3.5.
The affected versions and fixes
The GitLab remote code execution vulnerability affects self-managed GitLab CE/EE versions from 19.2 before 19.2.8, 19.3 before 19.3.5, and 19.4 before 19.4.2. GitLab says that when no specific deployment type is named, all deployment types are affected, meaning administrators should not assume they are exempt based on whether they use Omnibus, source, Helm charts, or another supported installation method. GitLab.com is already running the patched version, and GitLab Dedicated customers do not need to take action, according to the company’s release notes.
Patch status at a glance:
- Vulnerability: CVE-2026-97229
- Issue type: Integer overflow in the CI/CD Regular Expression Compiler
- Severity: Critical, CVSS 10.0
- Potential impact: Unauthenticated arbitrary code execution on the GitLab server
- Affected products: Self-managed GitLab CE/EE
- Affected versions: 19.2 before 19.2.8, 19.3 before 19.3.5, and 19.4 before 19.4.2
- Fixed versions: 19.2.8, 19.3.5, and 19.4.2
- Cloud status: GitLab.com patched; GitLab Dedicated customers do not need to act
The central issue is not only that attackers may be able to run code. It is where that code could run. GitLab servers often hold source code, merge requests, CI/CD variables, deploy keys, runner connections, package registry data, and links into production delivery workflows. A successful GitLab exploit against a self-managed server can therefore put more than one application at risk, especially if the instance is connected to automated build, test, and deployment pipelines.
Why the CI/CD compiler flaw matters
The vulnerable component parses, compiles, and evaluates regular expressions in project pipeline configuration files. GitLab said insufficient validation of regular expressions created a condition in which a crafted expression could trigger arbitrary code execution. That makes the flaw especially sensitive for organizations that allow broad project creation, public interaction, or external contribution workflows on self-managed GitLab instances.
The unauthenticated nature of the issue raises the urgency. Many vulnerabilities require a valid account, a privileged role, or a user action before exploitation is possible. This advisory describes a condition in which an unauthenticated user could reach code execution, which reduces the barrier for attackers if an affected instance is exposed to the internet.
For defenders, the risk also extends into trust boundaries. GitLab is not just a web application; it is often a central control plane for software delivery. If an attacker gains execution on that server, incident responders may need to consider whether CI/CD secrets, runner tokens, access tokens, deploy credentials, protected variables, build artifacts, and repository contents were exposed or abused. GitLab’s advisory does not provide exploit code or indicators of compromise, so teams should pair patching with log review and credential-risk assessment rather than waiting for more visible signs.
Administrators should patch before investigating edge cases
GitLab’s recommendation is direct: affected self-managed installations should upgrade to a fixed version as soon as possible. The company also notes that the patch includes database migrations, which may affect the upgrade process. Single-node instances will experience downtime while migrations complete before GitLab restarts, while multi-node instances can apply the patch without downtime if proper zero-downtime upgrade procedures are used.
That operational detail matters because it can tempt teams to delay a GitLab security patch until a maintenance window. For a CVSS 10.0 GitLab security issue with a potential unauthenticated path to server-side code execution, the safer approach is to schedule an emergency change, notify development teams, and document any downtime rather than allowing an exposed instance to remain vulnerable.
A practical response plan should include:
- Identify exposed self-managed GitLab instances. Prioritize internet-facing systems, systems reachable from partner networks, and instances that allow broad user registration or external project interaction.
- Confirm the running version. Any CE/EE instance in the affected 19.2, 19.3, or 19.4 ranges should be scheduled for immediate upgrade.
- Upgrade to the current fixed release line. Use 19.4.2, 19.3.5, or 19.2.8 depending on the supported branch and compatibility requirements.
- Plan for migration impact. Single-node deployments should expect downtime; multi-node environments should follow GitLab’s zero-downtime process where available.
- Review logs after patching. Check web, Rails, Sidekiq, runner, and system logs for suspicious pipeline activity, unusual CI/CD configuration changes, unexpected child processes, or abnormal access patterns.
- Assess credential exposure. If there is any sign of compromise, rotate CI/CD variables, deploy keys, runner authentication material, project access tokens, personal access tokens, and other secrets linked to the instance.
The patch should come first. Investigation is important, but a live vulnerable server can keep creating new evidence, new access, and new risk while defenders are still collecting logs.
The release also fixes several other security issues
CVE-2026-97229 is the headline flaw, but it is not the only issue addressed in the same GitLab patch update. GitLab’s release notes list 24 security fixes across critical, high, medium, and low severity categories. The additional fixes include a high-severity cross-site scripting issue in syntax highlighting, a high-severity authorization issue in downstream pipeline creation, and a high-severity permissive regular expression issue that could affect repository file access and CI/CD pipeline behavior.
That broader set of fixes reinforces the case for upgrading rather than trying to isolate one component. Security teams sometimes ask whether a particular feature must be enabled before a bug is relevant. For this release, GitLab’s own guidance is to upgrade affected installations to the latest fixed version, and the advisory states that unspecified deployment types should be considered affected.
The release notes also show how several issues touch areas that matter to software delivery integrity: protected branches, CI/CD pipelines, repository file access, Duo Agent Platform behavior, package registry permissions, project imports, and access-control checks. Even when those secondary vulnerabilities are not maximum-severity, they can become meaningful in combination with weak internal segmentation, broad developer permissions, or unmonitored automation tokens.
Recent GitLab flaws add pressure on defenders
The latest GitLab code execution vulnerability follows a period of heightened attention on GitLab security issues. BleepingComputer reported that GitLab had recently addressed another maximum-severity issue, CVE-2026-85706, and that CISA added that earlier flaw to its Known Exploited Vulnerabilities catalog after exploitation was observed. The same report noted that CISA has flagged multiple GitLab flaws abused in attacks since November 2021.
That history does not prove that CVE-2026-97229 is being exploited, and GitLab’s advisory does not state that exploitation is underway. It does, however, explain why defenders should move quickly. Public-facing development platforms are high-value targets because they can provide source code access, credential access, and a route into deployment systems from one compromised service.
The business impact can be larger than a single server outage. If attackers tamper with pipeline definitions, steal protected variables, or gain access to deploy credentials, responders may need to validate build integrity, review release artifacts, and examine downstream environments. For organizations that use GitLab as the backbone of DevSecOps, a GitLab exploit can turn into an incident across engineering, security, operations, and compliance.
What happens next
GitLab says security-fix issues are made public in its issue tracker 90 days after the release that patched them. Until more technical detail becomes public, administrators should avoid relying on exploit-specific detection and instead focus on confirmed exposure, version status, and signs of abnormal CI/CD activity.
Security teams should also use this event to check whether GitLab patch notifications reach the right owners. GitLab provides patch notification options, including release feeds, and critical releases may require coordination among platform engineering, application teams, security operations, and change-management owners.
For now, the clear action is to apply the GitLab security patch. Self-managed GitLab CE/EE installations in the affected ranges should move to 19.4.2, 19.3.5, or 19.2.8, with internet-facing systems first and post-upgrade monitoring close behind. The combination of unauthenticated access, server-side code execution, CI/CD proximity, and maximum severity makes this one of the GitLab security issues administrators should not leave for a routine maintenance cycle.
