
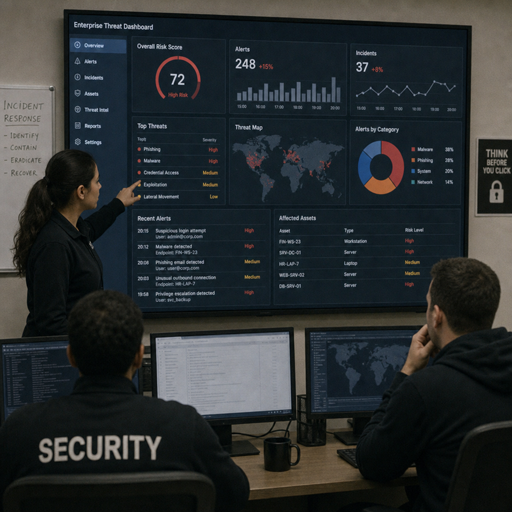
Enterprise defense software helps organizations detect threats, reduce operational risk, protect sensitive systems, and respond faster when something goes wrong. The best choice is not always the tool with the longest feature list; it is the one that fits your risk profile, compliance needs, internal workflows, and security maturity. This comparison explains the main categories of enterprise security tools, what to evaluate, and how to connect software decisions with practical corporate defense strategies.
What should enterprise defense software actually do?
Enterprise defense software should give security, IT, risk, and leadership teams a clearer view of threats across the business and a reliable way to act on them. At a minimum, it should support enterprise threat detection, investigation, response, reporting, and ongoing risk reduction. For larger software providers and complex organizations, it may also need to support business risk management, customer assurance, compliance evidence, and audit defense solutions for enterprise software providers.
In practical terms, the software should help answer three questions every day: what is happening, what matters most, and what should we do next? If a platform creates more alerts than insight, it can overwhelm teams instead of protecting them. Strong enterprise defense software turns noisy signals into prioritized action.
The main categories of enterprise defense tools
Enterprise defense is not one product category. It is usually a stack of security software solutions working together across endpoints, identities, networks, cloud environments, applications, data, and governance processes. Understanding the categories makes comparison easier because each tool solves a different part of the defense puzzle.
Threat detection and response platforms
Threat detection and response tools monitor activity across systems and look for suspicious behavior. They may include endpoint detection and response, network detection and response, cloud detection, user behavior analytics, or broader detection platforms that centralize signals from many sources.
These tools are valuable when an organization needs faster investigation and response. Instead of relying only on preventive controls, they assume threats may still get through and focus on finding them quickly. For enterprises with distributed teams, hybrid infrastructure, or sensitive customer data, enterprise threat detection is often one of the most important parts of the security stack.
Security information and event management
Security information and event management platforms collect logs and events from many systems in one place. They help teams correlate activity, search historical records, create alerts, and generate reports for internal or external review.
A SIEM can be powerful, but it needs thoughtful tuning. Without proper rules, data sources, and response processes, it can become a large repository of security noise. When implemented well, it supports both daily monitoring and longer-term investigations.
Governance, risk, and compliance tools
Governance, risk, and compliance platforms help organizations manage policies, controls, assessments, evidence, vendors, exceptions, and audit requirements. They are especially useful for connecting technical security work to business risk management.
For enterprise software providers, these tools can also support audit defense solutions for enterprise software providers by organizing evidence, mapping controls, tracking remediation, and preparing responses to customer or regulator requests. This does not replace legal, compliance, or security expertise, but it can make audit readiness more repeatable and less chaotic.
Identity and access security
Identity tools control who can access systems, data, and applications. They may include single sign-on, multi-factor authentication, privileged access management, identity governance, and access review workflows.
Identity is central to enterprise defense because many incidents involve compromised credentials, excessive permissions, or weak access processes. A strong identity program reduces exposure before an attack and helps investigators understand who did what after an event.
Vulnerability and exposure management
Vulnerability management tools identify weaknesses in applications, devices, cloud assets, and infrastructure. More advanced exposure management platforms may add asset context, exploit likelihood, ownership, and business impact.
The key is prioritization. Enterprises rarely fix every issue immediately, so the software must help teams decide which vulnerabilities create the most meaningful risk. Good prioritization considers severity, asset importance, exploitability, internet exposure, and compensating controls.
Comparison criteria that matter most
A polished demo can make almost any platform look impressive. A better comparison starts with the outcomes your organization needs and the friction your teams experience today. The right criteria should reveal whether the tool will improve real operations, not just add another dashboard.
Use this checklist when comparing enterprise defense software:
- Coverage: Does it protect the systems, users, cloud services, applications, and data that matter most?
- Detection quality: Does it reduce false positives and surface meaningful threats with useful context?
- Response workflow: Can teams assign, investigate, escalate, document, and resolve issues inside the platform or through integrations?
- Risk alignment: Does it connect technical findings to business risk management priorities?
- Compliance support: Can it organize evidence, map controls, and support audits without excessive manual work?
- Integration depth: Does it work with existing enterprise security tools, ticketing systems, identity platforms, and cloud environments?
- Scalability: Can it handle enterprise data volume, organizational complexity, and future growth?
- Usability: Can security analysts, risk teams, IT owners, and executives each get the view they need?
- Reporting: Does it provide clear reporting for leadership, auditors, customers, and internal stakeholders?
- Total operating effort: How much configuration, tuning, training, and maintenance will it require after purchase?
The strongest platforms usually perform well across several of these areas, but few are perfect everywhere. A tool that fits your workflows and integrates cleanly may deliver more value than a broader product that your team struggles to operate.
How do enterprise security tools compare by business need?
Enterprise security tools compare best when grouped by the problem they are meant to solve: detecting active threats, reducing exposure, managing access, proving compliance, or coordinating response. A large enterprise may need all of these capabilities, while a growing organization may start with the areas that carry the highest business risk. The most effective comparison is not “which tool is best?” but “which tool closes the most important gap?”
For example, an organization with repeated phishing incidents may prioritize identity protection, email security, and endpoint response. A software provider facing intensive customer security reviews may focus on control evidence, audit readiness, secure development visibility, and policy management. A company expanding into cloud infrastructure may need cloud posture management and workload protection before adding more traditional network tools.
This is why enterprise defense software should be evaluated against real scenarios. Create a shortlist of likely incidents and operational demands, then test how each platform supports them. Can the team trace an alert to the affected user and system? Can the tool show whether a critical asset is exposed? Can evidence be exported clearly for an audit? Can leadership understand the business impact without reading raw logs?
Building a practical evaluation framework
A clear evaluation framework prevents the buying process from becoming subjective. It also helps security teams explain recommendations to finance, legal, procurement, and executive stakeholders. Start with risk, then move toward capabilities, integration, usability, and long-term operating value.
1. Define your risk profile
Before comparing vendors, define what you are defending. List your most important assets, business processes, data types, customer obligations, and operational dependencies. Include known pain points such as slow investigations, manual audit preparation, poor asset visibility, alert fatigue, or inconsistent access reviews.
This step keeps the selection grounded. If customer trust and audit readiness are major concerns, compliance workflow and evidence management may matter as much as detection features. If ransomware resilience is the priority, endpoint visibility, backup coordination, identity hardening, and response automation may rise to the top.
2. Map features to outcomes
Feature lists can be misleading when they are reviewed in isolation. A product may advertise automation, analytics, dashboards, and integrations, but those features only matter if they improve a specific outcome.
Create a simple mapping table:
|
Business need |
Required capability |
Practical test |
|---|---|---|
|
Faster incident response |
Alert triage and case management |
Investigate a simulated high-risk alert |
|
Audit readiness |
Evidence collection and control mapping |
Produce a sample control evidence package |
|
Reduced exposure |
Vulnerability prioritization |
Identify top risks on critical assets |
|
Stronger access control |
Identity review and privileged access workflows |
Review excessive permissions for key systems |
|
Executive visibility |
Risk-based reporting |
Generate a leadership-ready risk summary |
This approach makes the evaluation more concrete. It also reduces the chance of choosing tools based on impressive but nonessential features.
3. Test integrations early
Integration claims deserve careful review. Many security software solutions say they connect with common enterprise systems, but the depth of integration can vary. A basic data import is not the same as a reliable two-way workflow that supports daily operations.
During evaluation, test integrations with the systems you actually use. Look at identity providers, cloud platforms, endpoint agents, ticketing tools, asset inventories, communication channels, and reporting systems. If integrations require heavy custom work, the long-term cost may be higher than expected.
4. Include the people who will use it
Security leaders may care about coverage and strategy, while analysts care about investigation speed, IT teams care about ownership and remediation, risk teams care about evidence, and executives care about decisions. A good evaluation includes each of these viewpoints.
Invite hands-on users into demos and proof-of-concept testing. Ask them where workflows feel clear and where they create friction. Enterprise tools fail when they look strong in procurement but weak in daily use.
Corporate defense strategies need more than software
Corporate defense strategies work best when technology, process, governance, and culture support each other. Software can detect suspicious activity, enforce access controls, organize evidence, and highlight risk, but it cannot decide priorities on its own. People still need ownership, escalation paths, response playbooks, executive support, and regular review.
A practical strategy should include:
- Clear ownership for assets, risks, controls, and incidents.
- Documented playbooks for common events such as compromised accounts, malware alerts, data exposure, and vendor concerns.
- Regular access reviews for sensitive systems and privileged roles.
- Risk-based vulnerability remediation that focuses effort on the most important exposures.
- Audit-ready evidence habits so documentation is gathered continuously, not rushed at the last minute.
- Executive reporting that connects security activity to business impact.
The best enterprise defense software supports these habits instead of replacing them. It should make good processes easier to follow and weak processes easier to see.
Common comparison mistakes to avoid
Many organizations make the same mistakes when evaluating enterprise defense software. They compare too many products at once, overvalue broad feature claims, or underestimate the internal work required to deploy and operate a platform.
One common mistake is buying for the most advanced future state before the team has the basics in place. Advanced analytics and automation can be useful, but they depend on clean data, clear workflows, and trained users. Another mistake is ignoring reporting needs until after implementation. If leadership, auditors, customers, or board stakeholders need regular updates, reporting should be tested during evaluation.
It is also risky to treat compliance and security as separate tracks. Compliance evidence can reveal control weaknesses, and security events can create audit implications. Tools that connect these activities help teams defend the business more coherently.
Choosing the right fit
The right platform depends on your current maturity and your next meaningful improvement. A smaller enterprise security team may need consolidation, automation, and managed support. A mature team may need deeper analytics, custom workflows, and stronger cross-functional reporting. A software provider serving enterprise customers may place extra weight on audit defense solutions for enterprise software providers, customer assurance, and repeatable evidence collection.
As you compare options, score each product against your most important scenarios rather than generic market labels. Look for tools that reduce manual effort, clarify ownership, improve detection, and strengthen business risk management. Just as importantly, choose software your teams can realistically operate.
Enterprise defense is not a one-time purchase. It is an ongoing capability built from the right technology, disciplined processes, and clear business priorities. When enterprise defense software is selected with that full picture in mind, it becomes more than another security platform; it becomes part of a stronger, more resilient operating model.
