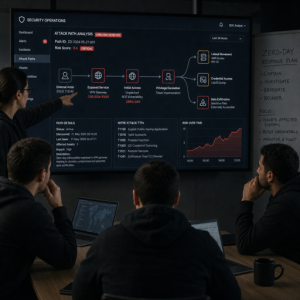
Zero-day vulnerabilities are security flaws that are unknown to the vendor, unpatched in the wild, or newly disclosed before defenders have a reliable fix. Because
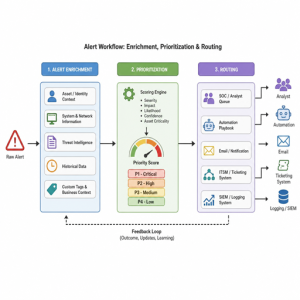
Automated alert triage helps security teams sort, enrich, prioritize, and route security alerts without relying on analysts to manually review every signal from scratch. It
Threat hunting works best when analysts can ask better questions of their data, test hypotheses quickly, and preserve evidence as an investigation develops. Open source
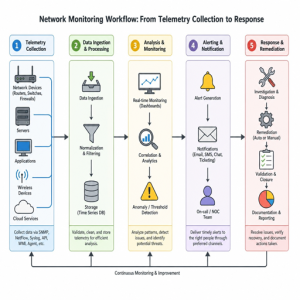
Detecting network anomalies and breaches means finding unusual behavior in network traffic, systems, identities, and devices before that behavior becomes a larger security incident. A
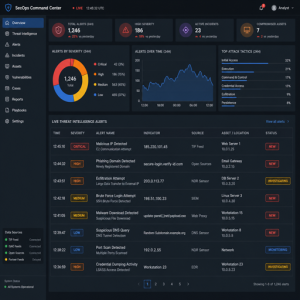
Real-time threat intelligence feeds give security teams a continuous stream of information about active and emerging cyber threats. They help organizations spot malicious indicators, understand
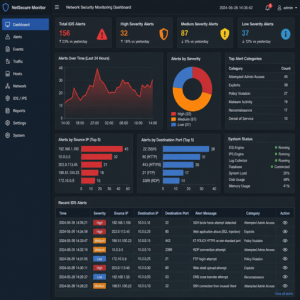
An intrusion detection system, or IDS, is a security monitoring tool that watches network traffic, systems, or applications for signs of suspicious activity. In practical
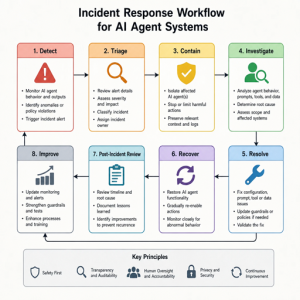
Open source incident response playbooks give teams a practical starting point for handling security incidents without writing every procedure from scratch. They are especially useful
Advanced network threat detection is the practice of finding suspicious activity across traffic, identities, endpoints, cloud environments, and applications before it becomes a damaging incident.
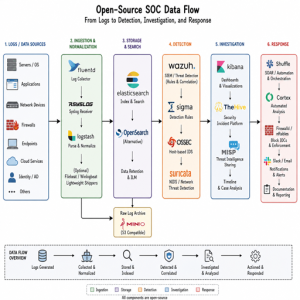
An open-source SOC is a security operations center built with community-driven, transparent, and customizable technologies instead of relying entirely on proprietary platforms. The goal is
Open-source security analytics gives teams a practical way to collect security data, investigate threats, and build monitoring workflows without starting from a blank page. The

 ossim