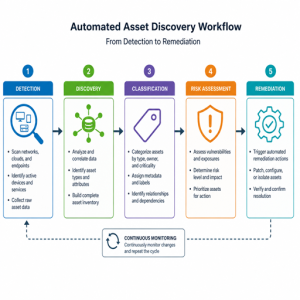
You cannot secure what you cannot see. Automated asset discovery gives security and IT teams a living inventory of devices, cloud resources, applications, users, services,
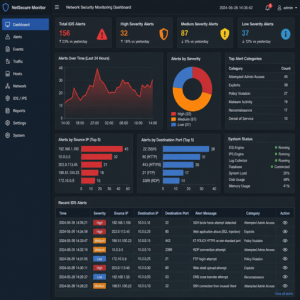
An intrusion detection system, or IDS, is a security monitoring tool that watches network traffic, systems, or applications for signs of suspicious activity. In practical
Open-source security analytics gives teams a practical way to collect security data, investigate threats, and build monitoring workflows without starting from a blank page. The
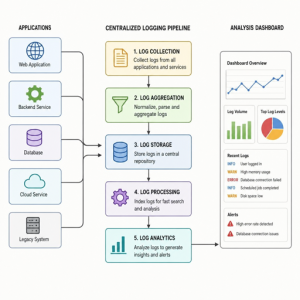
Logs are the running record of what your systems, applications, devices, and users are doing. Open-source log management systems help teams collect those records in
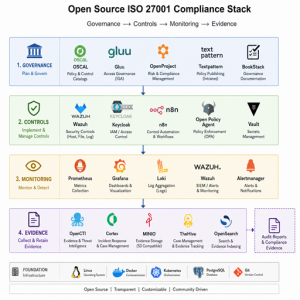
ISO 27001 can be supported with open source, but not by tools alone. The standard is about building and operating an information security management system,
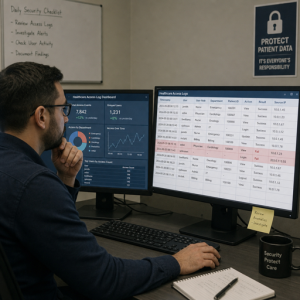
HIPAA compliance log management is the practice of collecting, protecting, reviewing, and retaining system activity records for environments that create, receive, maintain, or transmit electronic
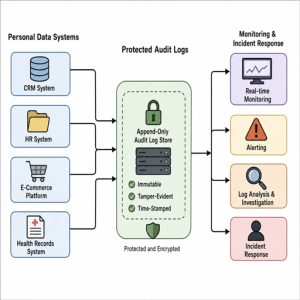
GDPR data protection logging is not a single technical standard you can install; it is a risk-based way of recording, protecting, reviewing, and retaining evidence
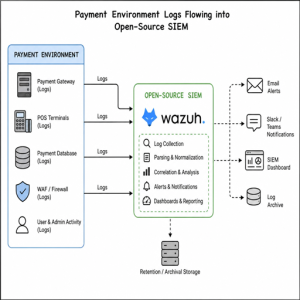
PCI-DSS compliance using open-source SIEM is about turning raw security logs into evidence, alerts, and repeatable processes that support payment-card protection. An open-source SIEM can
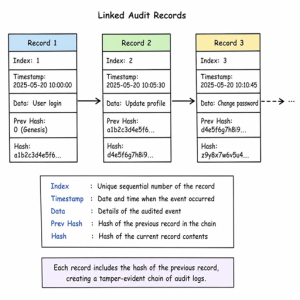
Immutable audit trails are tamper-resistant records that show what happened, when it happened, who or what initiated it, and whether the record has changed since
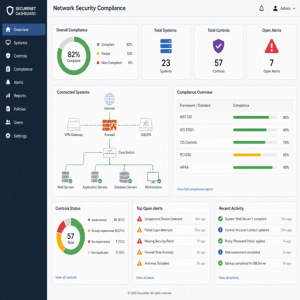
Regulatory compliance for network security is the process of aligning your network controls, policies, monitoring, and documentation with the laws, industry rules, and security standards